Private by design.Protected by hardware.
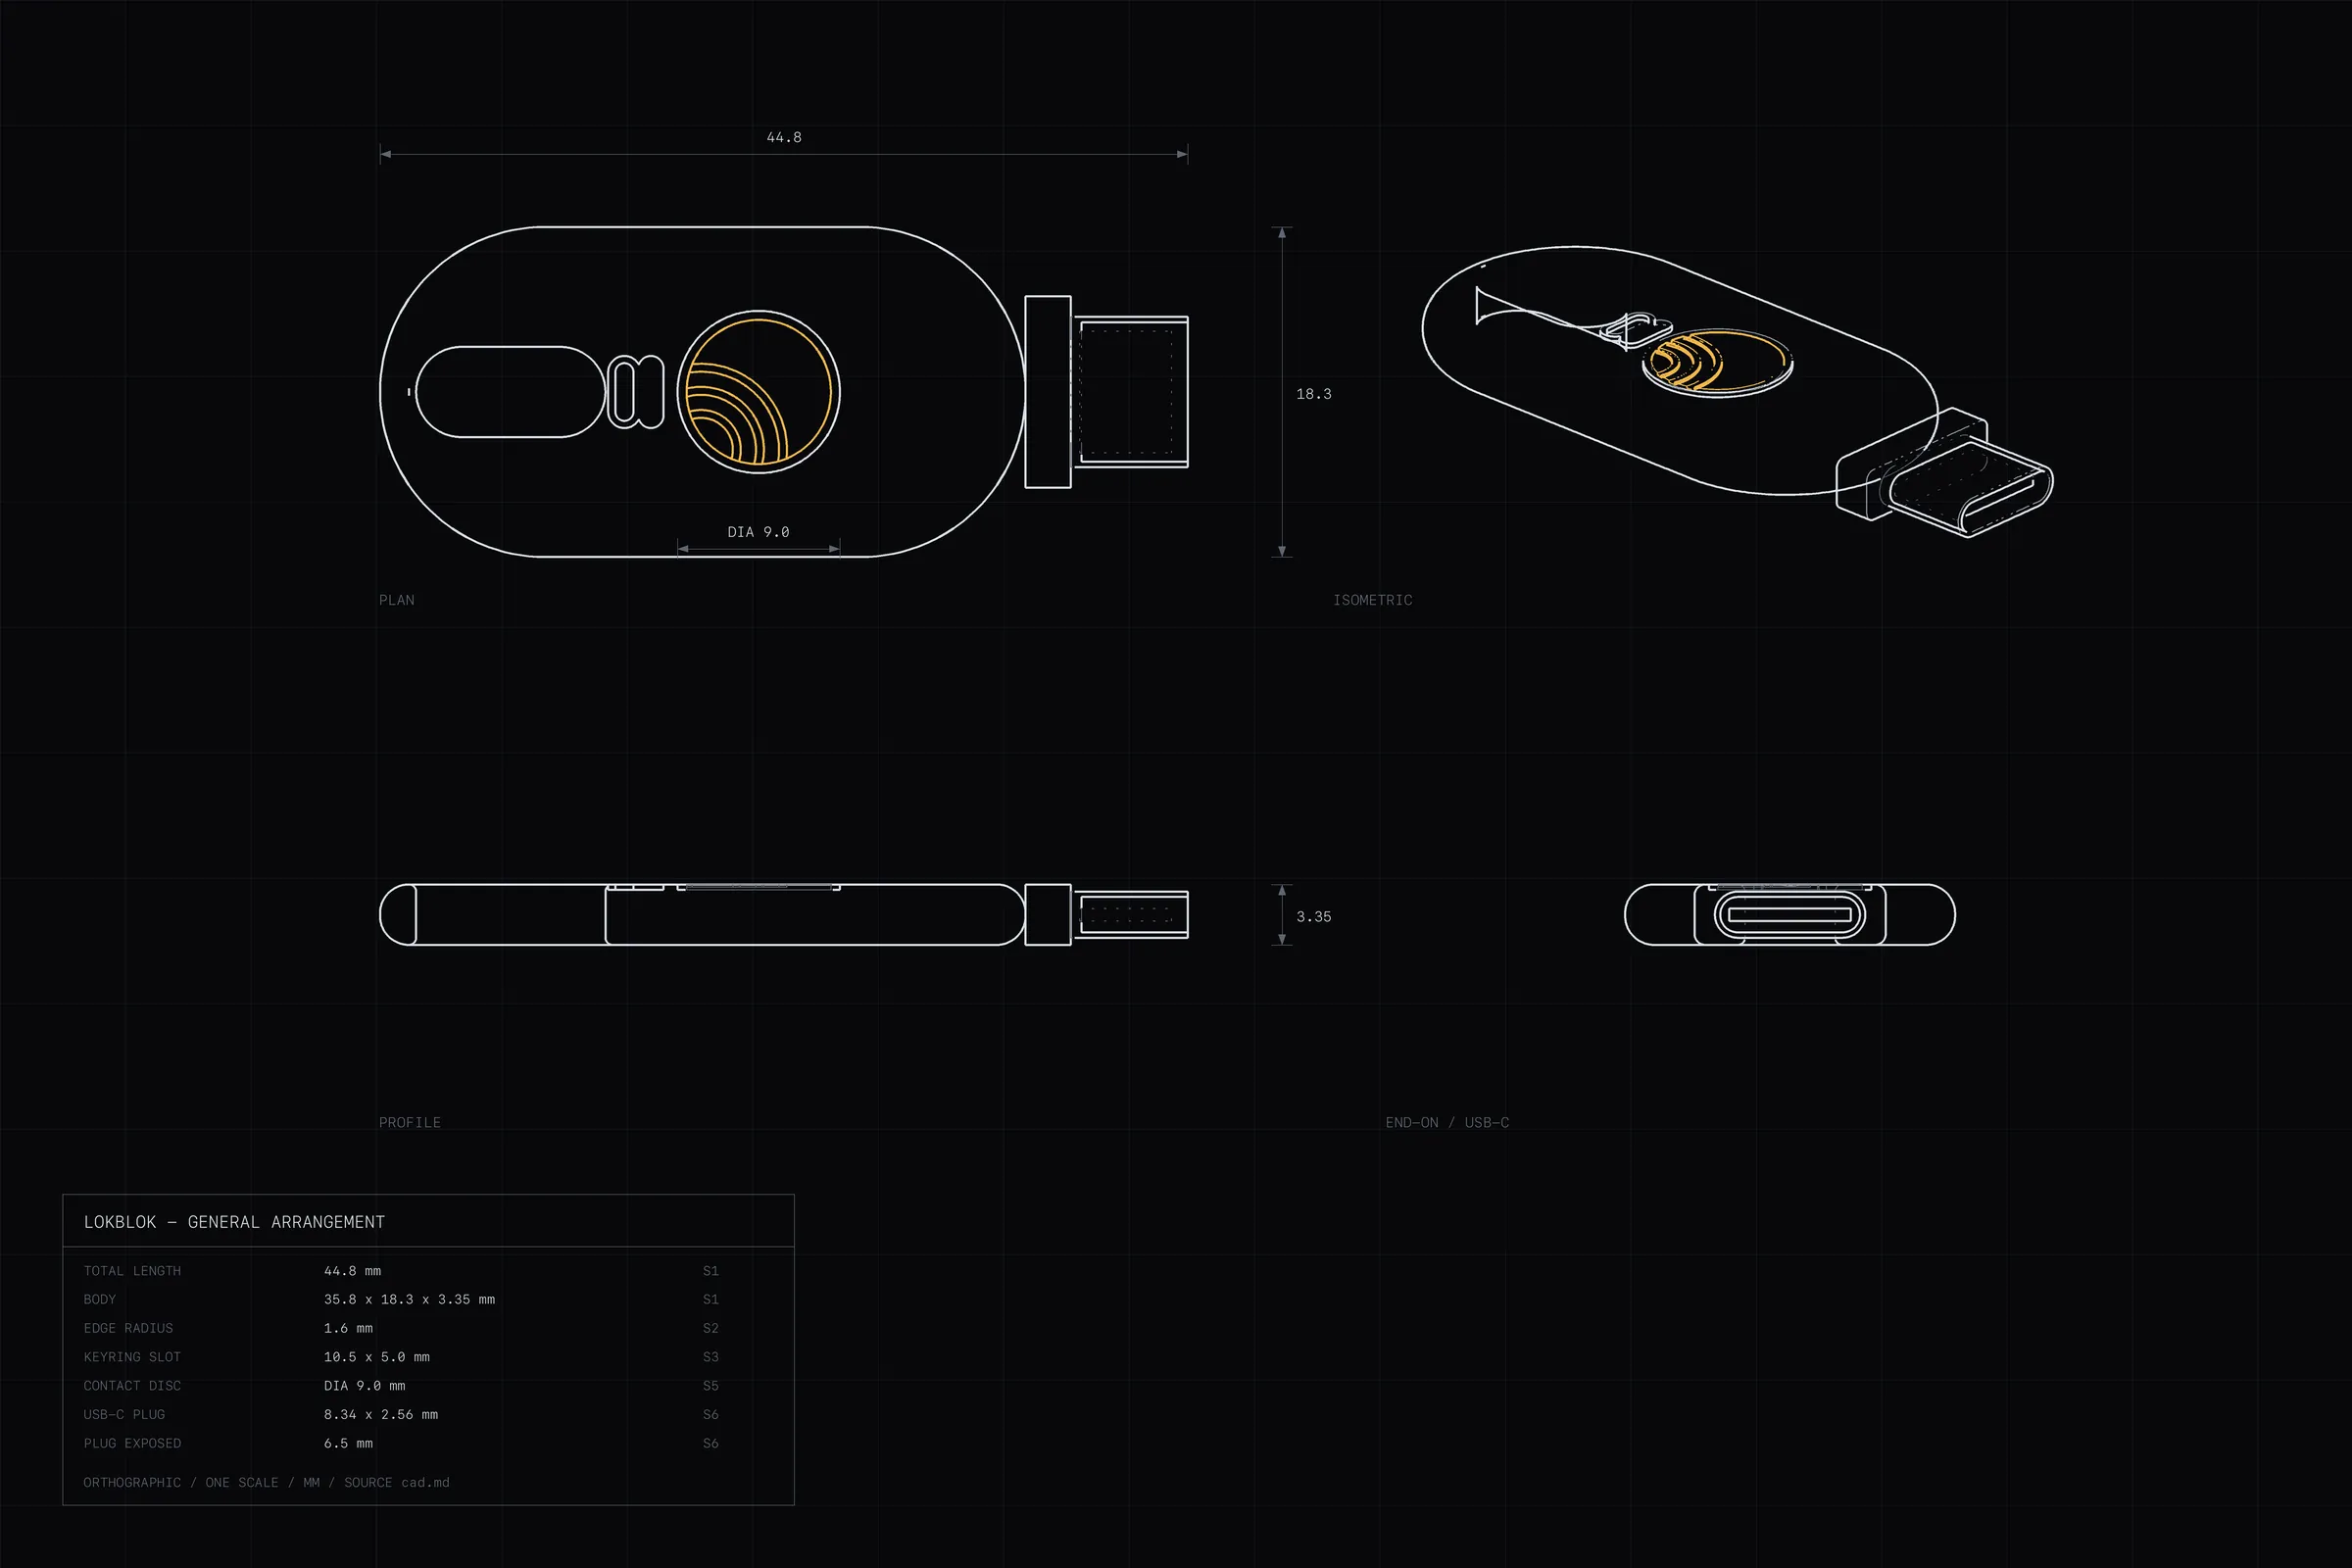
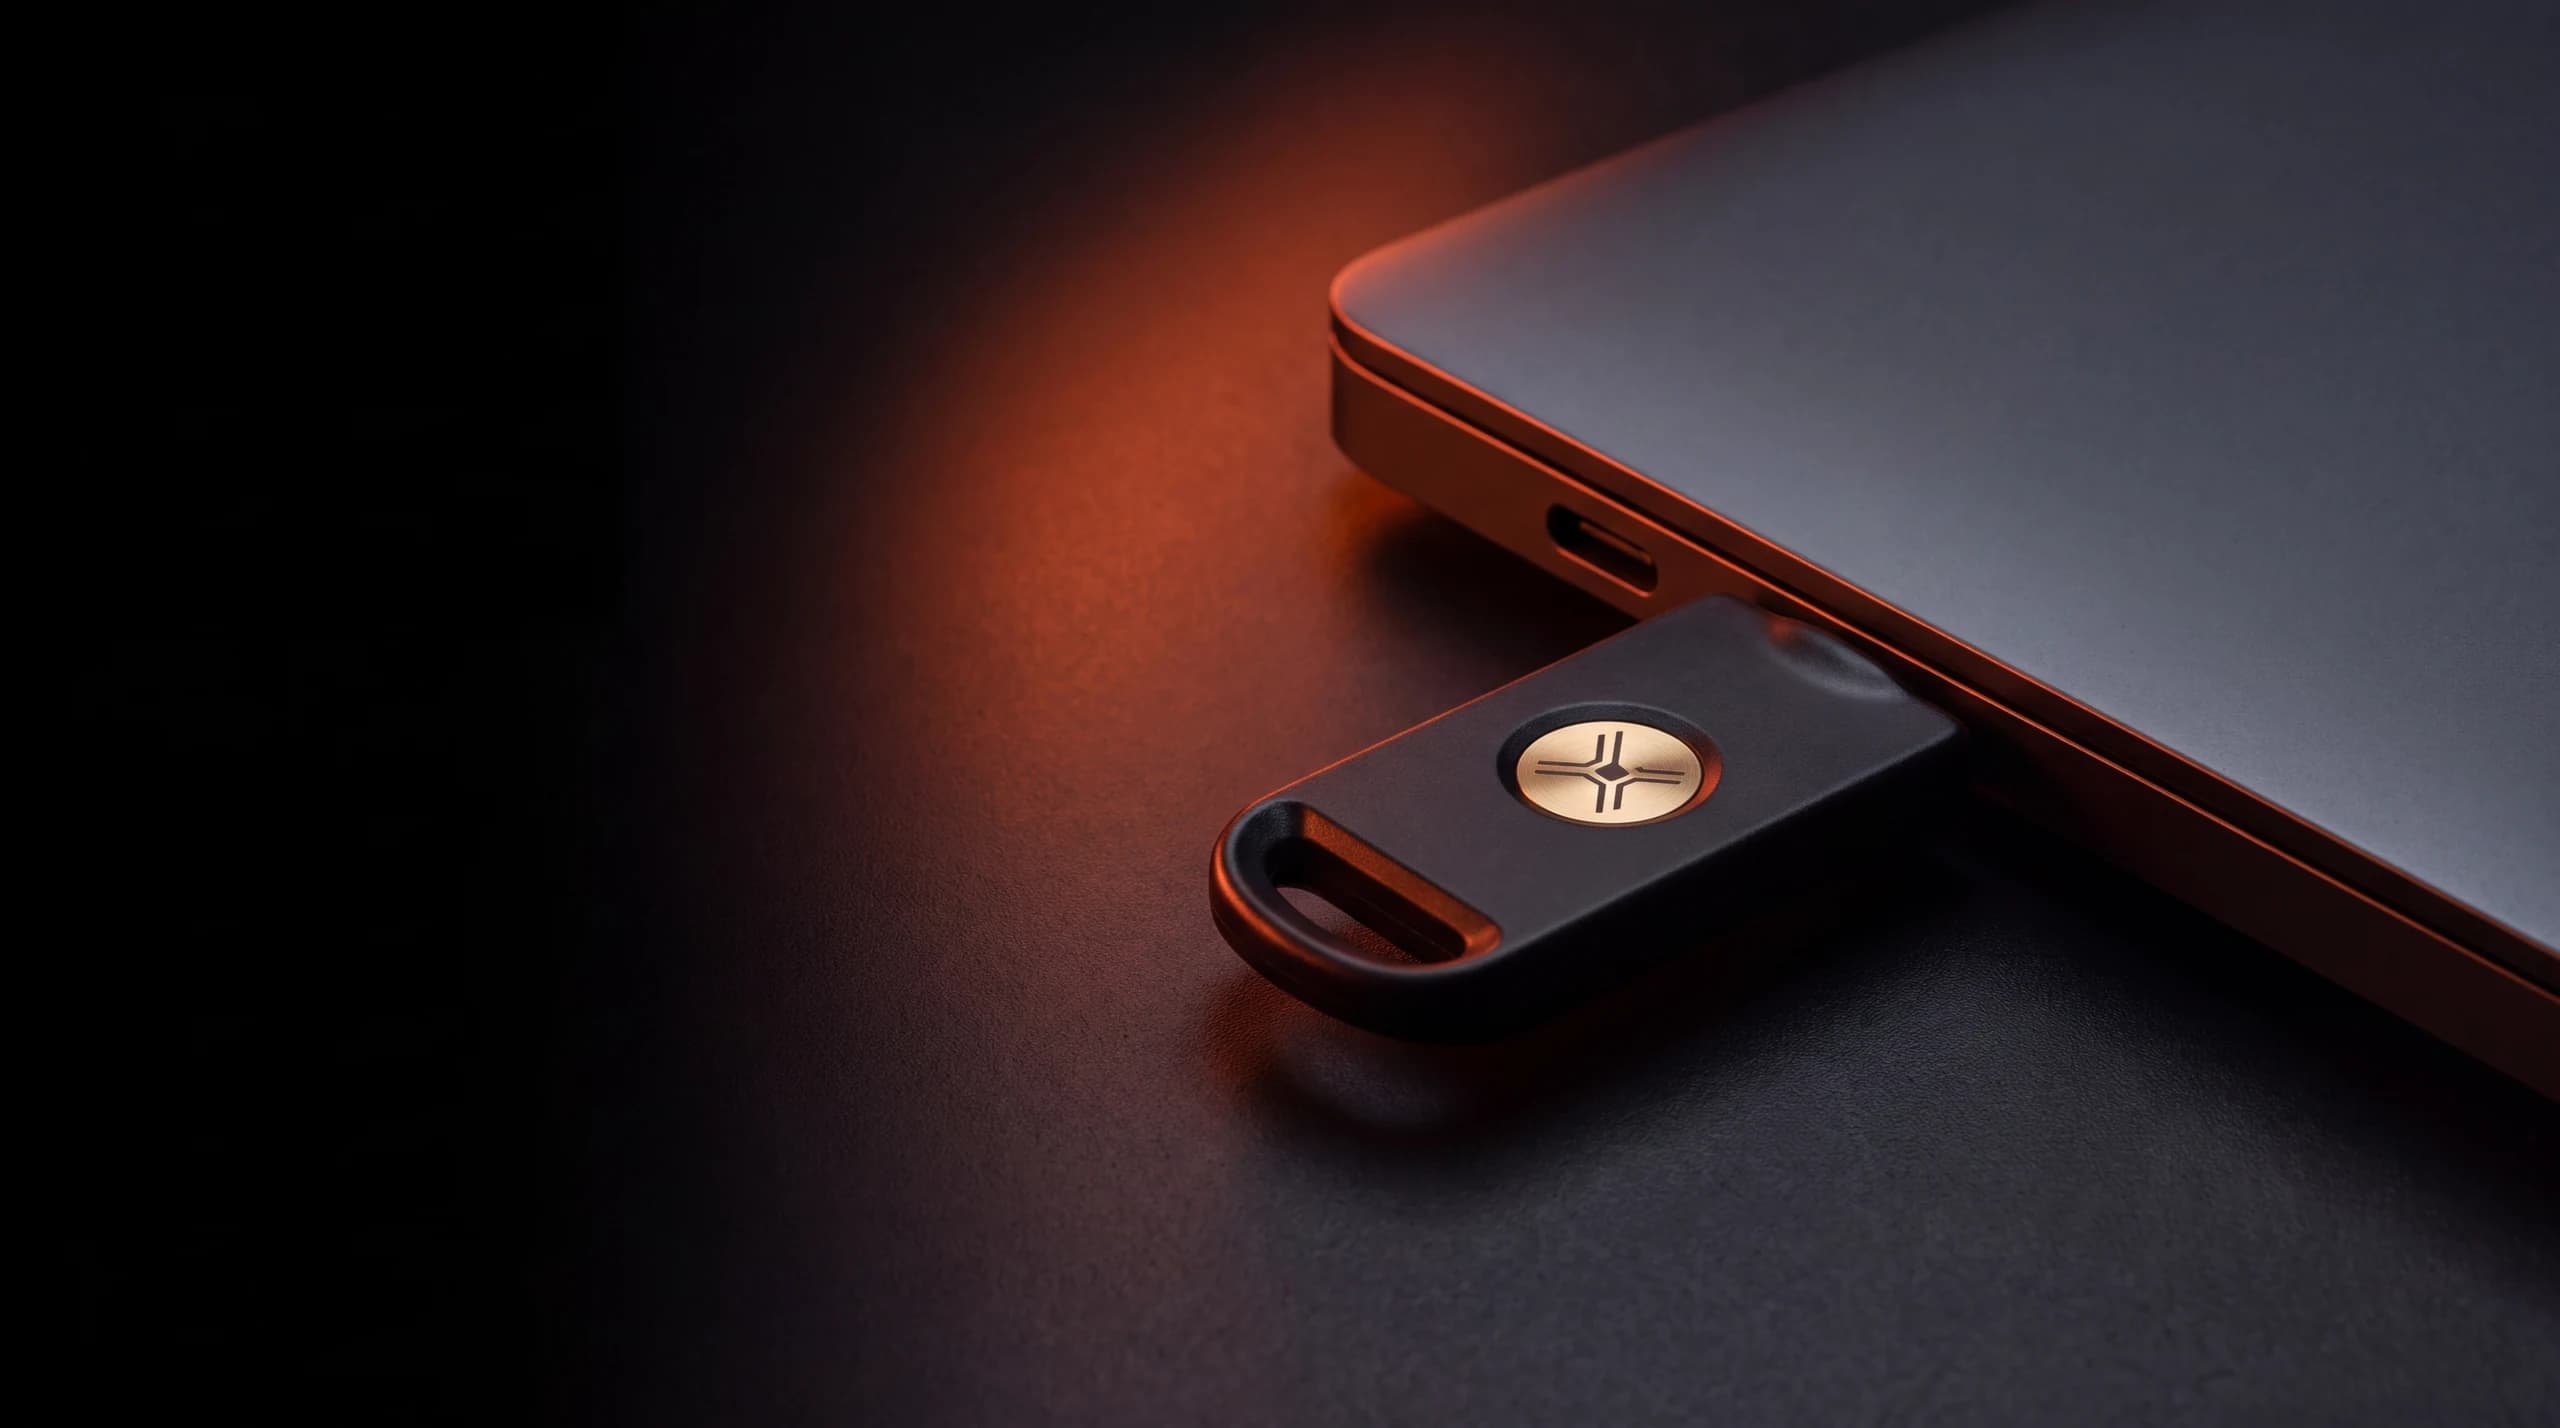
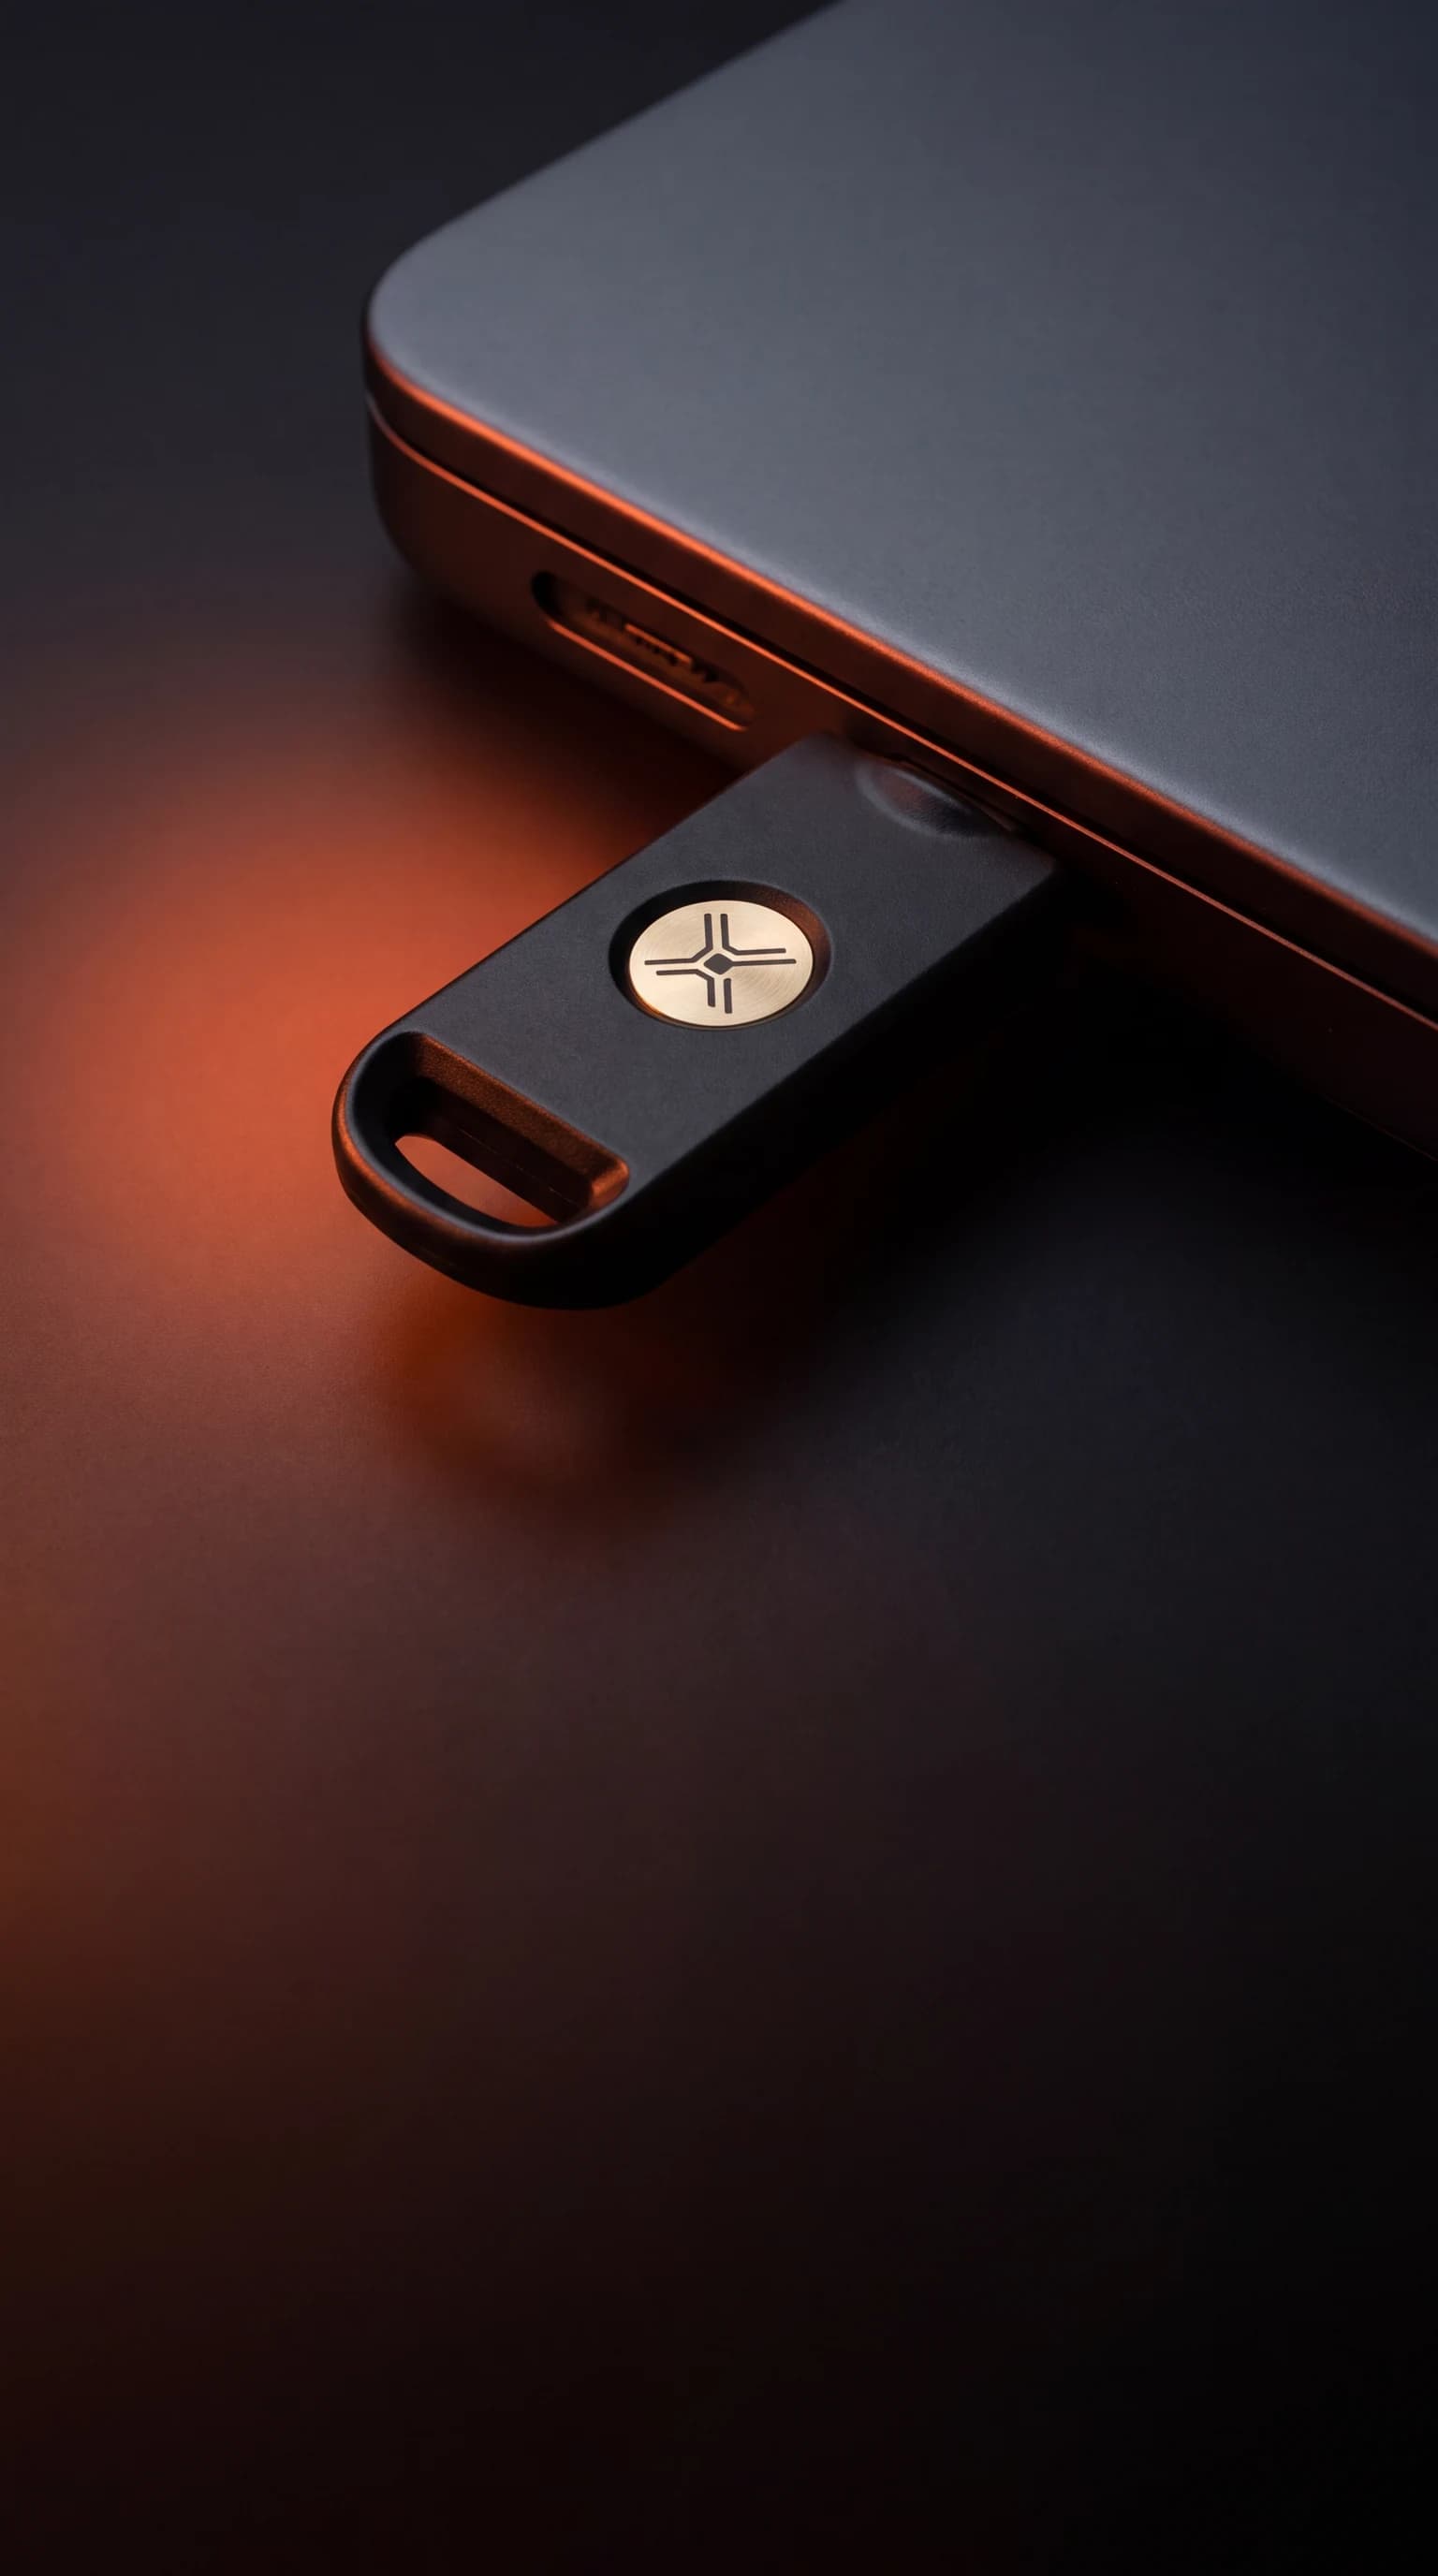
Protected storage and controlled access, anchored by the ToughKey physical key — more than a password between sensitive information and whoever holds the device. Primids pairs hardware custody with encrypted storage and secure communications.
What is Primids?
- Product
- Primids is a platform for encrypted storage and secure communications, paired with ToughKey hardware.
- Physical key
- ToughKey is the public hardware key; Key enrolment issues keys.
- Intended users
- Individuals, owner-led small businesses, and real-estate brokerages.
- Status
- Early access is via the waitlist; recovery, permissions, and audit are live systems.
interactive spider
Seven ways secrets leak
Passwords Get Copied
A password can be copied, shared, phished, or recovered from the cloud. If the only lock on sensitive files is a string someone else can type, possession of that string is enough. Primi treats a copied credential as exposure, not proof of authority.
SEVERED BYHARDWARE POSSESSION
Sensitive files need stronger control.
Passwords can be copied. Devices can go missing. Teams change. Give sensitive files hardware-backed protection and access controls you can manage.
- A password is only one layer. Add account MFA and hardware-backed file protection.
- A lost key needs a recovery process. Revoke the key and follow authorised recovery steps.
- Teams change. Access should be managed. Use roles and permissions to control who has access.
Protect what matters. Control who gets access.
Bring encrypted storage, key management and organisation controls together.
- Protect sensitive files Use encrypted storage with ToughKey.
- Manage team access Set roles and permissions.
- Trace security activity Review audit history.
Possession should not equal access.
THE PRINCIPLE
Possession of a password, a laptop, a notebook, or a departed account is not the same as authority to open what they used to protect. Primi puts a physical ToughKey key and explicit policy between holding the object and opening the files. Fear named the stake; the model that follows is how authority is granted, recorded, and recovered.
Meet the Primi security model.
A user on an approved device presents the ToughKey physical key. Primi policy checks identity, role, and permission. The request is powered by LokBlok security technology, then protected information may open, and the event is recorded. Seven nodes, one path. The physical key's public name is ToughKey.
03 / 07 · KEY
A user on an approved device presents the ToughKey physical key.
More than a security key.
ToughKey sits at the centre of a product system: protected storage, users and roles, permissions, Key enrolment, recovery, and audit history. Key enrolment is how keys are received, registered, assigned, replaced, and recovered. Recovery, permissions, and audit are a live system; early access is via the waitlist. The combination is the product, not the key alone.
01 / 05 · KEY
ToughKey sits at the centre of a product system: protected storage, users and roles, permissions, Key enrolment, recovery, and audit history.
Secure. Control. Recover.
Three pillars, one system.
01
02
03
Recovery, permissions, and audit run as live systems. Not three products — three views of the same model.
What sits behind physical authority.
Sensitive work sits behind a physical key, explicit permission, and a recorded event — files, documents, privileged access, and high-risk approvals. Each surface needs the ToughKey key and Primi policy before protected information opens; possession alone is not enough. Digital asset access is a specialised capability for a later release.
Files
Approved user, ToughKey, recorded event.
Documents
Not on a copied password or stolen laptop alone.
Privileged access
Administrative access that still needs physical authority.
Approvals
High-risk approvals that possession of an inbox cannot finish.
Powered by LokBlok.
Primi is the experience. LokBlok is the security technology underneath it. Physical authority. Explicit permission. Controlled access. Recorded events. One controlled path. No password alone decides authority. Architecture detail: lokblok.co.
Strong security should survive a lost key.
Recovery is a live Primi system: revoke a lost ToughKey, verify authority, enrol a replacement through Key enrolment, restore legitimate access, and record the event — operational strength with policy and audit, not unattended self-serve hardware on your desk today.
- STEP 01
ToughKey is active.
- STEP 02
Key reported lost.
- STEP 03
Access revoked.
- STEP 04
Authority verified.
- STEP 05
Replacement enrolled through Key enrolment.
- STEP 06
Legitimate access restored.
- STEP 07
Event recorded.
Same product. Different work.
One Primi product under three audience overlays — not three SKUs. Same ToughKey, Key enrolment, protected storage, control, recovery, and audit history; different work language for personal files, owner-led teams, and brokerage transaction files. Choose the path closest to your work.
Small Business
Owner-led teams with explicit users, keys, and offboarding.
Secure storage for small businessesReal-Estate Brokerages
Transaction files and a reseller conversation.
Security for real-estate brokeragesSecurity you can inspect.
Architecture, implementation, testing, and certification are different things.Review how the physical key, policy, recovery, and audit are described, including residual risk, in one place. Serious buyers can inspect the architecture without treating a badge as proof. Security architecture and assurance status
Request early access
Tell us what you need to protect. We’ll follow up with next steps.